Detection Engineering in 2026: The Complete Lifecycle (Sigma, YARA, DaC & AI)
Detection engineering is more than writing SIEM rules. Learn the 6-phase lifecycle, the detection-as-code model, and why identity is the new battlefield.

Detection engineering is more than writing SIEM rules. Learn the 6-phase lifecycle, the detection-as-code model, and why identity is the new battlefield.
Unleash the power of your command line with Nushell, the modern shell for cyber security professionals. Analyze data more efficiently with Nushell today!
Transform raw logs into leads in this practical cyber investigation guide. We solve the Hack the Box Brutus Sherlock and show you how to hunt down attackers.
Learn how to flip the script on attackers in this comprehensive guide on active defense and cyber deception for cyber security analysts.
Discover the power of C2 hunting and learn to hunt for C2 servers so you can stay ahead of the hackers. This guide teaches you C2 hunting using Shodan.
Learn how to effectively manage all your cyber threat intelligence data sources using a collection management framework. Increase CTI efficiency today!
Discover the must-know cyber security actions you can take to defend your business from the latest threats by unpacking the courses of actions (CoA) matrix.
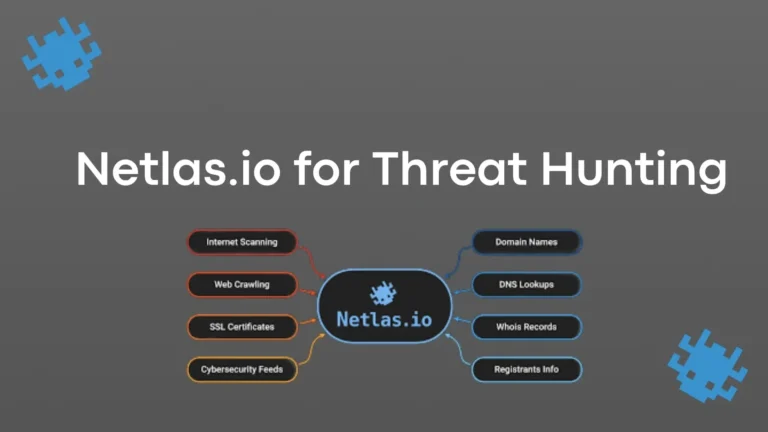
Discover netlas.io, a powerful suite of tools to enrich your threat hunts, add threat intelligence to your investigations, Discover netlas.io, a powerful suite of tools to enrich your threat hunts, add threat intelligence to your investigations, and map your attack surface.
Learn why malware configuration parsing is an essential skill for any threat hunter, plus how to use a malware configuration parsers to do this automatically.
Discover the new cyber security notetaking app that integrates with your organization’s tools and is an effective copilot for all your investigations.
Make your threat hunting process more efficient by integrating MISP and CrowdStrike Falcon EDR so you can automate uploading your IOCs for detection.
Learn how to create a Jupyter Notebook that you can use to query your MISP instance. This will drastically speed up your threat intelligence operations!
Discover what Jupyter Notebooks are and learn how to create your own to structure your threat hunting workflow and improve your efficiency.
Learn to create your own Python packages using the Python module Poetry. This lets you easily share your threat hunting tools with the community.
Discover how to extract valuable information from JSON to analyze it and turn it into threat intelligence or IOCs to hunt for in your environment.