Detection as Code: A Pipeline That Won’t Flood Your SOC
Learn detection as code with a four-stage pipeline to validate, translate, test, and deploy Sigma rules, plus the mistakes that sink SOC migrations.

Learn detection as code with a four-stage pipeline to validate, translate, test, and deploy Sigma rules, plus the mistakes that sink SOC migrations.
Discover how the Lazarus Group became the world’s most successful cybercrime syndicate, and the detection gaps most security teams still miss.
Learn how Sigma rules, modifiers, and pySigma power platform-agnostic detection engineering and threat hunting, plus the pitfalls tutorials skip.
North Korean remote workers pass interviews, then extort you. Learn the DPRK remote IT worker hiring pipeline, TTPs, and seven detection opportunities.
Learn when your business is ready for CTI for SMB, which controls come first, and a 60-day roadmap to run threat intelligence on a real budget.
Most people think breaking into cyber threat intelligence (CTI) is a skills problem. It is not. It is a signal problem. I came up through
Volt Typhoon hides inside your own tools and waits. Learn how this Chinese APT pre-positions in critical infrastructure and how to hunt it in your network.
Learn how to build a threat intelligence program for your SMB using free tools like OTX and MISP. Get actionable CTI for SMBs this afternoon.
Detection engineering is more than writing SIEM rules. Learn the 6-phase lifecycle, the detection-as-code model, and why identity is the new battlefield.
Cut through the noise. Discover the four CTI certifications that actually get you hired, in the right order, without wasting time or money.
How MCP servers are transforming CTI workflows in 2026, which tools are worth your time, and how to secure the new attack surface they create.
One phone call brought down M&S and cost £300M. Here’s who Scattered Spider is, how they operate, and the controls that stop them.
Learn the difference between data, information, and intelligence. Discover how CTI analysts can brief stakeholders in language that drives action.
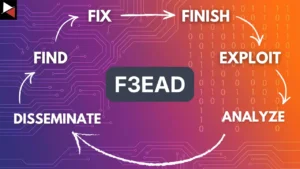
Discover how to use the F3EAD intelligence loop to enhance your cyber threat intelligence processes and produce actionable insights in this complete guide.
Want to become a CTI analyst? This guide maps the 3-stage pathway from IT support to SOC to cyber threat intelligence. Start your journey here.