Skip to content
No results
  • Learn
    • Dashboard
    • Learning Resources
  • Services
    • Business Consulting
    • Individual Coaching
  • Blog
  • Resources
    • Community Discord
    • Weekly Newsletter
    • GitHub Repositories
    • Community Resources
    • CTI Knowledge Self-Assessment
Kraven Security Logo
  • Learn
    • Dashboard
    • Learning Resources
  • Services
    • Business Consulting
    • Individual Coaching
  • Blog
  • Resources
    • Community Discord
    • Weekly Newsletter
    • GitHub Repositories
    • Community Resources
    • CTI Knowledge Self-Assessment
Kraven Security Logo
  • Threat Intelligence, Threat Hunting

Threat Intelligence vs Threat Hunting: What is the Perfect Pipeline?
Threat Intelligence vs Threat Hunting What is the Perfect Pipeline

Discover how to integrate your cyber threat intelligence with your threat hunting tasks to create the perfect pipeline and streamline your operations.
  • Adam Goss
  • 5 May 2023
  • 6 Comments
  • Threat Hunting, Custom Tooling

Python Threat Hunting Tools: Part 1 — Why?

Python Threat Hunting Tools Part 1 - Why?

Learn how to build your own threat hunting tools with Python in this new series! First, let’s find out why it is important to build your own tools.
  • Adam Goss
  • 1 May 2023
  • Career Advice and Training

Free vs Paid Cyber Security Training: The Secret to Career Success

Free vs Paid Cyber Security Training The Secret to Career Success

Training is vital for success in cybersecurity. Let's explore the options you have at your disposal and perhaps the best path to follow to achieve your goals.
  • Adam Goss
  • 24 April 2023
  • Threat Hunting

Hunting for Persistence with Cympire: Part IV — Startup Folder

Hunting for Persistence with Cympire - Startup Folder

Learn how attackers use the Windows Startup Folder to maintain persistence once they’ve compromised a machine. Then hunt for these malicious Startup Folder items.
  • Adam Goss
  • 17 April 2023
  • Threat Intelligence, Threat Hunting

How to Arm Yourself with Custom Sigma Rules

Lock & Load - Arming Yourself with Custom Sigma Rules

Discover how to create your own custom Sigma rules to hunt for the latest threats that are affecting your environment and thwart threat actors.
  • Adam Goss
  • 10 April 2023
  • 5 Comments
  • Threat Hunting

Hunting for Persistence with Cympire: Part III — Services

Hunting for Persistence with Cympire - Service Persistence

Learn how attackers use Windows services to maintain persistence once they’ve compromised a machine. Then see how to hunt for these malicious services.
  • Adam Goss
  • 3 April 2023
  • Threat Intelligence, Threat Hunting

How to Arm Yourself with Threat Intelligence

Lock and Load - Arming Yourself with Threat Intelligence

Learn how to use threat intelligence articles, the MITRE ATT&CK framework, and Sigma rules to perform threat-informed hunting using Splunk queries.
  • Adam Goss
  • 22 March 2023
  • 1 Comment
  • Threat Hunting

Hunting for Persistence with Cympire: Part II — Scheduled Tasks

Hunting for Persistence with Cympire - Scheduled Task Persistence

Learn how attackers use scheduled tasks to maintain persistence once they’ve compromised a machine. Then see how to hunt for these tasks.
  • Adam Goss
  • 6 March 2023
  • Threat Intelligence, Threat Hunting

MITRE ATT&CK Framework: Holy Bible of Threat Intelligence

Lock & Load I: The Holy Bible of Threat Intelligence

Let's explore the MITRE ATT&CK framework and find out why it's a must know tool for any cyber threat intelligence analyst looking to tackle the latest threats.
  • Adam Goss
  • 20 February 2023
  • 31 Comments
  • Threat Hunting

Hunting for Persistence with Cympire: Part I — Registry Run Keys

Hunting for Persistence with Cympire - Registry Run Persistence

Learn how attackers use Windows registry keys to maintain persistence once they’ve compromised a machine. Then see how to hunt for these malicious keys.
  • Adam Goss
  • 8 February 2023
  • Threat Intelligence, Threat Hunting

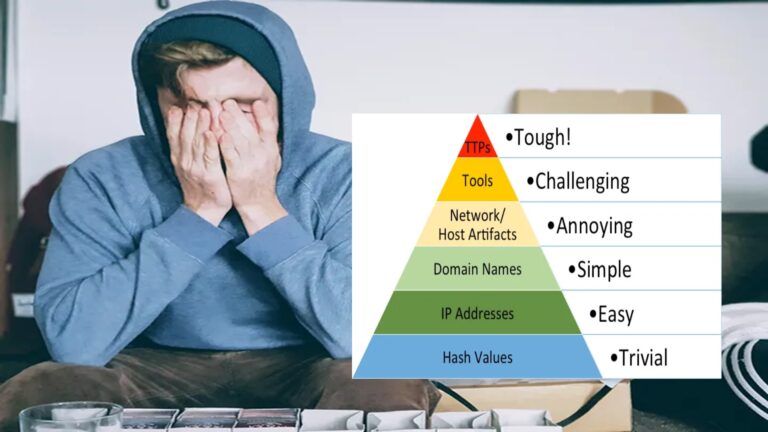
Elevate Your Threat Detections Using the Almighty Pyramid of Pain

Elevate your Threat Detections using the The Almighty Pyramid of Pain

Discover how to turn a bad guy's day into a nightmare using the Pyramid of Pain to elevate your threat detections and increase the cost on adversaries.
  • Adam Goss
  • 24 January 2023
  • 8 Comments
  • Threat Intelligence, Custom Tooling

Let Us Find Out Whodunit

Let Us Find Out Whodunit

Whodunit is a tool that can be used to identify the most likely Advanced Persistent Threat group responsible for an attack. Let's find out how to use it!
  • Adam Goss
  • 11 January 2023
  • Threat Hunting

Threat Hunting With Velociraptor III – Hunting Demo

Threat Hunting with Velociraptor III - Hunting Demo

Learn how to use Velociraptor’s threat hunting capabilities to identify malicious activity associated with real-world malware and threat actors in this demo.
  • Adam Goss
  • 8 November 2022
  • 1 Comment
  • Threat Hunting

Threat Hunting With Velociraptor II: Environment Setup

Threat Hunting With Velociraptor II - Environment Setup

Discover how to create a virtualized threat hunting environment and use Velociraptor as a threat hunting tool to sniff out malicious reverse shells.
  • Adam Goss
  • 26 October 2022
  • Threat Hunting

Threat Hunting With Velociraptor I – Introduction

Threat Hunting With Velociraptor I - Introduction

Learn what threats are, what threat hunting is, and the basic security requirements needed to start a threat hunting program in this series introduction.

  • Adam Goss
  • 18 July 2022
Prev
1 … 15 16 17 18 19
Next
Location
  • Basingstoke,
  • United Kingdom
Pages
  • Privacy Policy
  • Frequently Asked Question
  • Terms & Conditions
  • Code of Conduct

Copyright © 2026 - Kraven Security