Getting Started With Intelligence Requirements: A Full Guide
Discover how to create cyber threat intelligence requirements that help align your business objectives with your threat intelligence team's output.
Discover how to create cyber threat intelligence requirements that help align your business objectives with your threat intelligence team's output.
Australian court hacked, a formal ban on ransomware incoming, and Mandiant X account hijacked in triaging the week 006.
Discover the cyber threat intelligence lifecycle in this comprehensive guide. Learn the 6 stages of the lifecycle and how to apply them to your CTI operations.
Hackers abuse GitHub, FBI takes major shot at ALPHV ransomware, and the Lapsus$ hacker gets sentenced in triaging the week 005.
A definitive guide to cyber threat intelligence. Learn what cyber threat intelligence is and how it is used for proactive defense against the latest threats.
DNS vulnerabilities, cloud engineers rampage, and the UK at risk of catastrophic ransomware attack in triaging the week 004.
Discover why it is important to have clear definitions for key cyber threat intelligence concepts and how this series can be your reference guide.
Google Workspace vulnerabilities, a new version of Kali Linux, and Kraven Security’s website is now live in triaging the week 003.
We have officially launched the website. This interactive platform lets you learn all things cyber threat intelligence, threat hunting, and custom tooling.
China Influencers on the Rise, Space Agencies Under Attack, and Advent of Cyber 2023 Begins in triaging the week 002.
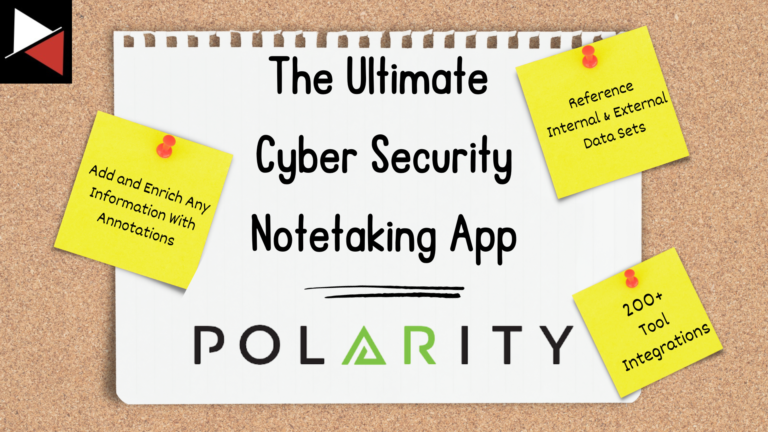
Discover the new cyber security notetaking app that integrates with your organization’s tools and is an effective copilot for all your investigations.
OpenAI turmoil, COO hacks hospital to boost sales, and Kraven Security starts a newsletter in triaging the week 001.
Make your threat hunting process more efficient by integrating MISP and CrowdStrike Falcon EDR so you can automate uploading your IOCs for detection.
Discover how to turn MISP attributes into Indicators of Compromise that you can export as a CSV file and upload to your security solution for detection.
Learn how to create a Jupyter Notebook that you can use to query your MISP instance. This will drastically speed up your threat intelligence operations!