Triaging the Week 014
New threat intelligence reports released, Russia moves to hacking the cloud, and NIST updates its cyber security framework in triaging the week 014.
New threat intelligence reports released, Russia moves to hacking the cloud, and NIST updates its cyber security framework in triaging the week 014.
Learn how to create and build your own Kubernetes cluster using Terraform, Ansible, and the power of infrastructure as code (IaC). Run K8s Locally Today!
Google open source AI tool, crackdown on LockBit ransomware, and new attacks that manipulate virtual assistants in triaging the week 013.
Discover the must-know cyber security actions you can take to defend your business from the latest threats by unpacking the courses of actions (CoA) matrix.
Big bounty offered for ransomware leaders, malware gets more sophisticated, and a critical vulnerability in Zoom in triaging the week 012.
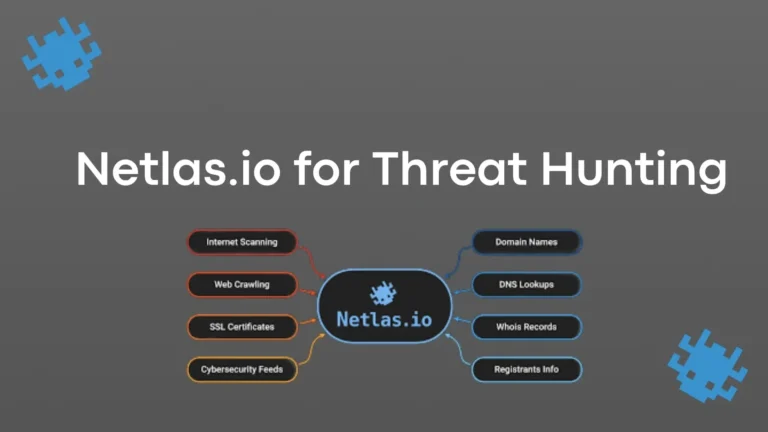
Discover netlas.io, a powerful suite of tools to enrich your threat hunts, add threat intelligence to your investigations, Discover netlas.io, a powerful suite of tools to enrich your threat hunts, add threat intelligence to your investigations, and map your attack surface.
New container escape, malware spreads with Facebook ads, and toothbrushes fight back in triaging the week 011.
Discover the top 5 real-world threat intelligence lifecycle challenges you will face and how to overcome them to produce actionable intelligence.
NSA steals data, Mercedes fumbles GitHub tokens, and the police hit the Bitcoin jackpot in triaging the week 010.
Learn why malware configuration parsing is an essential skill for any threat hunter, plus how to use a malware configuration parsers to do this automatically.
Malware abuses Discord, Australia imposes sanctions, and the Uber of cybercrime is revealed in triaging the week 009.

Learn about MITRE’s CTI Blueprints project. A revolutionary new CTI project that aims to help analysts deliver high-quality, standardized CTI reports.
New mitigations and with GrapheneOS and iShutdown scripts, top ransomware gangs to watch out for in 2024, and MacOS malware evades XProtect in triaging the week 008.

Learn the 3-stage indicator lifecycle, a model for turning raw data into actionable cyber threat intelligence for proactive defense and threat hunting.
DPKR steals all the crypto, X accounts are under siege, and China Cracks Apple’s AirDrop in triaging the week 007.