

Cyber threat intelligence is the latest evolution in traditional intelligence tradecraft and espionage – a discipline dating back to ancient times. To understand how the current threats you face have come to be, you must explore the history of cyber threat intelligence.
This guide aims to give you a quick overview of the significant historical events that led to the formation of cyber threat intelligence in the modern era. It covers the evolution of intelligence from antiquity to the Cold War, how the digital age affected intelligence work, and the current threat landscape.
The guide concludes with a breakdown of the threats dominating modern cyberspace and how cyber threat intelligence is pivotal to combating them. Let’s jump in!
Want to listen on the go? Check out this article in podcast form!
The Origins of Cyber Threat Intelligence
Intelligence can be defined as “knowledge and foreknowledge of the world around us—the prelude to decision and action…” (CIA). Collecting, analyzing, and disseminating this knowledge makes it valuable in supporting decision-making in security, warfare, and governance.
Throughout history, intelligence has been crucial for gaining a strategic advantage over rivals, whether in political maneuvering, economic competition, or business. However, perhaps where intelligence has seen the greatest use is in warfare.
There are references to the strategic use of intelligence in texts from ancient China (e.g., Sun Tzu’s The Art of War) and accounts of spies, scouts, and informants from various other ancient civilizations (e.g., Egyptian, Greek, and Roman). The first documented organized spy networks came from the Elizabethan era when the British empire grew more complex and required formalized intelligence-gathering methods, secret codes, surveillance, and deception.
This was led by Sir Francis Walsingham (Queen Elizabeth I’s spymaster), who ushered in the birth of “modern” intelligence in the 16th century. He pioneered the role of intelligence in trade, diplomacy, and warfare against enemies, foreign and domestic. Walsingham anticipated methods that would become routine only centuries later. He employed double agents, covert propaganda and disinformation, code-breaking, and agent provocateurs to advance English interests.
Despite the many advances in intelligence tradecraft he made, Sir Walsingham is best known for his part in the execution of Mary, Queen of Scots, in 1587 after she tried to provoke a Scottish rebellion against the monarch
Advancements in intelligence tradecraft stayed relatively dormant after Sir Walsingham’s passing. More advanced codes would be made and broken, other nation-states would gradually invest more in their intelligence capabilities (particularly those with civil unrest), and military intelligence played a role in the Napoleonic wars. Still, significant developments weren’t seen until the start of the 20th century when the world went to war.
Modern Intelligence
World War I re-invigorated the need for nation-states to have intelligence capabilities. Advancements in communication technology and the need to coordinate large military forces to act in unison across vast geographies led to the widespread usage of cryptographic methods to secure these communications.
Implementing this method required distributing codebooks to military personnel so they could decipher the messages they were receiving. British Military Intelligence (MI1) invested significant resources in capturing these codebooks so they could decrypt enemy communication. This involved human intelligence (HUMINT) and the newly formed signals intelligence (SIGINT), which involved capturing the enemy’s communications.
These efforts led to the decryption of the Zimmermann telegram in January 1917.
Zimmerman was the German Minister to Mexico and was caught offering United States territory to Mexico in return for joining the German cause. Several weeks later, the British presented the Zimmermann telegram to the U.S. Government to capitalize on growing anti-German sentiment in the United States. The American press published news of the telegram on March 1, and on April 6, 1917, the United States Congress formally declared war on Germany and its allies.
The Zimmermann Telegram impacted American opinion so much that it is regarded as the most consequential cryptoanalysis in history. You can learn more about the impact of secret codes in David Kahn’s excellent book The Codebreakers, which details the origins of GCHQ.
The use of intelligence and secret codes grew even more in WWII as the battlefield expanded and technology advanced. This war is the birthplace of many modern intelligence agencies, such as the British MI6 and the United States OSS (precursor to the CIA).
The most famous intelligence work from this era came out of Bletchley Park, the home of the British Government Code and Cypher School (GC&CS), a precursor to GCHQ. This team of expert cryptanalysts (code breakers) broke Germany’s Enigma code and turned the tide of the war using counter-intelligence and disinformation initiatives like the Double-Cross system.
There is a fantastic movie on the work done at Bletchley Park called The Imitation Game, featuring Benedict Cumberbatch and Keira Knightley.
Once WWII ended, the need for nations to have intelligence capabilities dwindled again until the Cold War between the United States and the Soviet Union (USSR) began to heat up in the 1980s. This war was shaped by the development of nuclear weapons and nuclear deterrence (Mutually Assured Destruction, MAD).
This led to a new style of warfighting involving proxy nations, covert espionage and sabotage operations, and the widespread adoption of counterintelligence.
The Cold War led nations to develop intelligence agencies specializing in counterintelligence and surveillance operations, like the British MI5, the Russian FSB, and America’s FBI, as well as their signals intelligence counterparts (GCHQ, TsIB, and NSA). It also led to significant advancements in surveillance technology, the stuff you see in James Bond movies.
However, at the end of the Cold War, intelligence was still grounded in the main INTs:
- HUMINT (Human Intelligence): Direct human interaction.
- SIGINT (Signals Intelligence): Content and metadata from communication mediums (e.g., telecommunications).
- IMINT (Image Intelligence): Information from images (e.g. ,satellites).
There was no (or very little) intelligence being gathered in cyberspace.
The Digital Age and Cyber Threat Intelligence
Between the 1960s and late 1980s, the Internet we know today only existed as a small network of interconnected computers between prominent Universities in the United States (ARPANET). This network expanded to the National Science Foundation Network (NSFNet), created by CERN, to include institutions in Europe, Australia, New Zealand, and Japan in 1988-89.
Then, in 1990, Tim Berners-Lee began writing the World Wide Web (the first web browser). This invention led schools, financial institutions, and businesses to adopt these interconnected networks. The Internet was born, and the widespread adoption led to the technology industry’s first big bubble (dot-com bubble) in the late 1990s.
The days of relying on covert human operations and spy gadgets are being replaced by big data, digital surveillance, and hacking. This shift from traditional espionage to online computers fundamentally changed intelligence work and led to the birth of cyber threat intelligence (CTI).
Nation-State Attacks
China was the first documented nation to adopt cyberspace as a new battlefield for intelligence and hacking. Starting in the mid-1990s and continuing throughout the 2000s, China conducted several primary cyber operations against the United States.
- Moonlight Maze (1996 – 1998): A series of data breaches of classified United States Government information from NASA, the Pentagon, military contractors, civilian academics, the Department of Energy (DOE), and numerous other American government agencies.
- Titan Rain (2003 – 2005): A series of attacks on the computer systems and network of United States defense contractors, including Lockheed Martin, Sandia National Laboratories, Redstone Arsenal, and NASA.
- Operation Aurora (2009 – 2010): A series of cyber attacks on dozens of top United States companies, including Google, Adobe Systems, Akamai Technologies, Juniper Networks, Rackspace, Symantec, Northrop Grumman, Morgan Stanley, and Dow Chemical.
The modus operandi for these operations was to steal sensitive data to use back in China for technological advancement. These early campaigns kick-started the evolution of CTI as government agencies and private sector companies needed insights into how they were being attacked.
Mandiant’s APT1 Report encapsulates these early cyber espionage campaigns. It was the first report to expose the inner workings of a sophisticated state-sponsored cyber-espionage unit. The report marked a turning point in public and governmental awareness of the scale and sophistication of cyber threats, ultimately influencing how organizations and nations approached cyber security defense and international cyber policy. It is the first piece of nation-state threat intelligence that was publicly available.
The revelations from the APT1 Report and other nation-state hacking activities spurred the creation of national-level Computer Emergency Response Teams (CERTs). These groups were responsible for coordinating the management of national cyber security incidents, often involving sharing intelligence about cyber threats with the public and private sectors.
Government and private sector collaboration in intelligence sharing led to the development of structured intelligence frameworks that empowered organizations to share threat intelligence more effectively. You can learn more about these frameworks in STIX/TAXII: A Full Guide to Standardized Threat Intelligence Sharing.
As nation-states developed their cyber capabilities, they shifted away from stealing intellectual property, trade secrets, and classified information and instead conducted cyber sabotage. This began with Stuxnet in 2010, where the United States and Israeli governments collaborated to develop and deploy a computer worm that disabled a key part of the Iranian nuclear program.
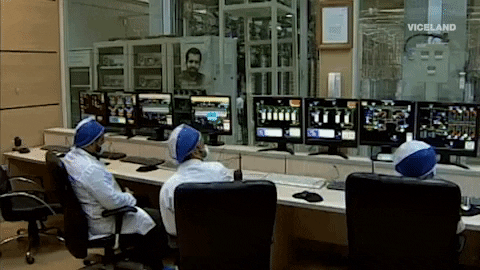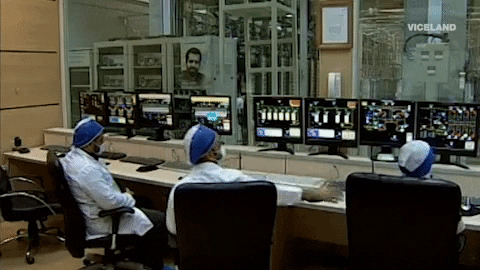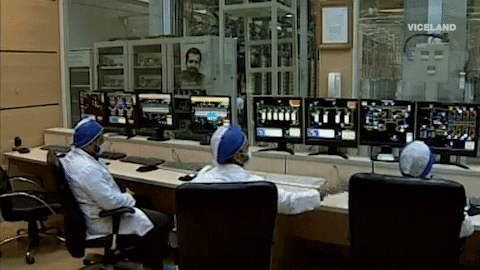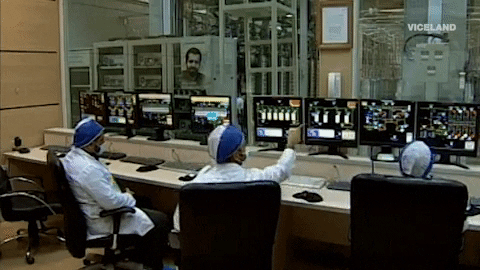
Stuxnet was the first time a cyber attack had targeted an Industrial Control System (ICS). Since then, Russia has conducted several cyber-sabotage operations against Ukraine, starting with an attack against Ukraine’s power grid in 2015 and continuing through to its war with Ukraine in 2020.
However, cyber sabotage has not been the only motive for nation-state actors. The self-isolated country of North Korea has used its cyber capabilities to target commercial businesses for revenge (2014 Sony hack) and financial gain (2016 Bangladesh bank heist). These attacks have been performed to protect the image of their regime and fund the nation’s destitute economy through cyber tradecraft.
North Korea has most recently attacked cryptocurrency exchanges in the United States, Japan, and South Korea, stealing over $659 million in 2024.
This is not to say that nation-states have moved away from traditional espionage; they just expanded their repertoire. The Russian disinformation campaigns around Brexit and the 2016 presidential election, along with sophisticated supply chain attacks like the Solar Winds hack in 2020 and XZ backdoor in 2024, highlight this.
The Rise of Cybercrime and Ransomware
Nation-states weren’t the only ones using cyber. Cybercriminals have been using cyber tradecraft for financial gain since the start of the Internet. This began with mass spam campaigns in the 1990s and 2000s that tried to defraud unsuspecting victims with scams like the Nigerian prince.
Cybercriminals also used cyber tradecraft to facilitate traditional criminal activities like money laundering, selling illicit materials, stalking, and assassinations. This led to the creation of various anonymous Internet marketplaces where users could buy or sell criminal services and illegal products (e.g., drugs, guns, etc.).
The most infamous was Silk Road, which became a $200 million operation between 2011 and 2013. Technological advancements like cryptocurrency, blockchain, and the dark web fueled its popularity.
Then, ransomware began to hit the scene in 2013 with CryptoLocker. At first, ransomware operated on a “spray and prey” business model, trying to infect as many victims as possible and charging a modest fee ($75 to $750) for decryption. There was no focus on how to apply pressure to a specific victim.
However, between 2016 and 2019, established cybercriminal gangs entered the ransomware business, and the ransomware payloads and digital extortion tactics were refined. These refinements included faster and stronger encryption, double extortion techniques, cryptocurrency laundering, and data exfiltration.
Since 2019, the ransomware business has become an entire ecosystem of professional criminal services. Initial access brokers, affiliates, developers, and data exfiltration teams all work together and take their cuts. Watch Securework’s Tim Mitchel talk to learn more about the ransomware ecosystem.
But ransomware didn’t just stop at targeting businesses. Cybercriminals have also targeted ICS systems and healthcare providers to extort them for money by leveraging the potential loss of life!
The most notable of these is the Colonial Pipeline attack in 2021, where the DarkSide ransomware gang forced the Colonial Pipeline Company to halt all pipeline operations and demanded 75 bitcoins (or $4.4 million). This attack was monumental in the United States government’s decision to invest more resources to fight cybercrime and improve critical infrastructure security.
The emergence of ransomware and its cost to businesses have raised organizations’ budgets for cyber security. Many organizations have invested in developing their CTI capabilities to manage their ransomware exposure and reduce the risk presented by modern cyber tradecraft.
The most recent emerging trend in cybercrime has been the rise of InfoStealer malware and its ecosystem. To learn more about this ecosystem, watch this excellent presentation by the Flare team.
So where are we now? Where does your work as a cyber threat intelligence analyst fit in?
Modern Cyber Threat Intelligence
That brings us to the modern era of threat intelligence. Nation-states are attacking ICS, performing supply chains, and attacking financial institutions. Meanwhile, ransomware gangs are leveraging people’s lives for money. It’s not a great place to be, but at least there isn’t a world war currently.
Here is where we find ourselves today:
- AI and machine learning: The use of AI for cyber offense and defense is in full swing. This lowers the barrier of entry for adversaries and makes it easier to build complex attack campaigns. On the other hand, CTI analysts are using AI and machine learning to support the processing and analysis of diverse data sources, making CTI teams more efficient.
- Increased sophistication of ransomware: The professionalization of the ransomware ecosystem makes it more sophisticated and complex to stop. It has become a threat to nearly every organization (e.g., business, government, and critical infrastructure) and requires intelligence to combat effectively.
- Emergence of InfoStealer malware ecosystem: The increasing sophistication of the InfoStealer ecosystem, combined with the shift to remote work, has made this commodity malware a significant threat to corporate environments and personal lives. Users can be easily tricked into inadvertently downloading InfoStealer malware, so proactive monitoring of credential data is needed to keep businesses safe.
- Shift left approach in software development: Software vulnerabilities are reported on an increasing basis every year. This has led to significant policy shifts urging developers to adopt memory-safe languages like Rust and Go, ensuring their products are secure by design. Vulnerability intelligence will continue to be crucial in helping organizations manage their attack surface.
- Increase of critical infrastructure targeting: Over the past decade, critical infrastructure has become a prime target for threat actors. This includes networks, transportation, telecoms, public health, energy, utilities, and more! Intelligence is required to help ensure this infrastructure is protected against those targeting it.
- Rise in supply chain attacks: The steady increase in supply chain attacks, whether through malicious packages or an adversary compromising a service provider, necessitates that organizations be more diligent about their third-party risks. Threat intelligence is needed to manage these risks effectively and counter modern cyber tradecraft.
These are the main challenges we face as CTI practitioners. You are responsible for providing intelligence so key stakeholders can make informed decisions about defending against these threats.
The days of intelligence being used exclusively by nation-states for espionage are long gone. It’s now time for everyone to use intelligence to navigate the risks of our digital world!
Conclusion
The history of cyber threat intelligence (CTI) is soaked in bloody wars, covert espionage, and technology booms. For much of its history, intelligence has been a power wielded by the few against the many. Nation-states have used it for diplomatic relations, to squash rebellions, and to win wars.
With the boom of the digital age, intelligence has become a tool for ordinary people to protect their digital lives and manage the risks their businesses face.
This guide describes the history of cyber threat intelligence that has led to the current threat landscape and the discipline of CTI. It concluded by highlighting the significant challenges we face as CTI practitioners and how the effective use of intelligence can combat them. Good luck!




Frequently Asked Questions
How Did Intelligence Begin?
Intelligence has its roots in the earliest days of civilization, evolving as a vital tool for survival, warfare, and diplomacy. Even before written records, ancient societies recognized the value of gathering and analyzing information about adversaries, allies, and the natural environment.
Intelligence gathering was already established in ancient Egypt, Greece, and China. Rulers employed scouts and spies to monitor enemy movements and assess the strengths and weaknesses of neighboring kingdoms. In his classic work The Art of War, the renowned strategist Sun Tzu emphasized the importance of espionage, declaring that knowledge of one’s enemy was essential for success in battle.
Who is the Father of Intelligence?
Sir Francis Walsingham (Queen Elizabeth I’s spymaster) is considered the father of intelligence. In the 16th century, he pioneered the role of intelligence in trade, diplomacy, and warfare against enemies, foreign and domestic. The intelligence tradecraft he developed during this time, such as double agents, covert propaganda and disinformation, code-breaking, and agent provocateurs, became routine practices centuries later.
When Did Cyber Threat Intelligence Start?
Cyber threat intelligence (CTT) began its evolution in the early 2000s after China launched a series of cyber attacks against United States defense contractors, universities, and companies (e.g., Moonlight Maze, Titan Rain, and Operation Aurora). These campaigns aimed to steal sensitive data to use back in China for technological advancement and led to the first publicly documented nation-state threat intelligence.
Government agencies (e.g., GCHQ, NSA, etc.) and private sector companies needed insights into how they were being attacked, and modern CTI grew from this requirement. Mandiant’s APT1 report encapsulated these early years of CTI and the cyber tradecraft being used.
How Old is CTI?
While the foundational concepts of threat intelligence have roots in military and geopolitical history, the formalized discipline of Cyber Threat Intelligence (CTI) is a more recent development. The term began to be discussed in the early 2000s as the cyber threat landscape grew in complexity.
However, CTI gained significant traction and widespread recognition in the cyber security industry following the public release of the Mandiant report on APT1 in 2013. This report detailed a sophisticated cyber-espionage campaign and highlighted the need for a structured and intelligence-led approach to cyber security.
What is Nation-State Threat Intelligence?
Nation-state threat intelligence is the collection and analysis of information about cyber threats posed by government-backed hacking groups. These highly sophisticated and well-resourced adversaries, often referred to as Advanced Persistent Threats (APTs), typically target other nations for espionage, intellectual property theft, or to disrupt critical infrastructure. The primary goal of this intelligence is to understand the motivations, capabilities, and tactics of these state-sponsored actors to better predict and defend against their attacks. This specialized field of cyber threat intelligence is crucial for national security and the protection of key industries.

