

In today’s complex cyber landscape, organizations face a critical challenge: determining which threats deserve their limited resources and attention. Threat profiling offers a systematic solution, cutting through the noise to identify and prioritize adversaries most likely to target your organization.
Rather than attempting to defend against everything, which is impossible, threat profiling helps you understand your real threats, how they operate, and where to focus your defenses. It transforms abstract threats into concrete threat profiles you can act on, shifting from reactive security to proactive defense.
This guide will walk you through a structured process for identifying, analyzing, and documenting the threats that matter most, empowering you to improve your security posture and resource allocation dramatically.
Want to listen on the go? Check out this article in podcast form!
What is Threat Profiling?
Threat profiling is a structured and repeatable approach to identifying and prioritizing relevant cyber threats that your organization should address. These threats could be adversaries, malware strains, or attack techniques, whatever your organization must prioritize defending against.
It is one approach to implementing threat-informed defense and is often performed as part of a holistic threat or risk assessment process. For instance, threat profiling is a part of Intelligence Preparation of the Cyber Environment (IPCE). This analysis technique is made up of four stages:
- Determine the Environment
- Determine Environmental Factors
- Evaluate Potential Threat Actors
- Determine Course of Action

Although it sounds simple, performing IPCE for a large organization can be challenging. As such, cyber threat intelligence (CTI) teams often focus on one of the core components, such as evaluating potential threat actors (threat profiling) or determining a course of action (threat modeling). This allows them to perform more targeted analysis with a quick turnaround, although it may lack the whole environmental context.
It is essential to note that threat profiling is not the same as threat modeling. These two techniques often get confused because they are both threat-centric and relate to threat-informed defense. However, they are designed to help an analyst answer a different set of questions.
- Threat Profiling focuses on understanding threats in the general context of the threat landscape. What are they, who are they, what motivates them, and how do they typically operate? It is outward-facing, answering what is out there that could impact my organization.
- Threat modeling matches the threat’s capability against your organization’s assets, network infrastructure, and security controls to determine how they would exploit your organization. It is inward-facing, answering how my organization would be targeted.
Both are key analysis techniques that can inform and complement one another as part of IPCE analysis. You should use both to help inform your organization’s security controls and resource prioritization. However, it is essential to remember that they are designed to answer different threat questions.
With this in mind, let’s look at other common misconceptions about threat profiling.
Common Misconception About Threat Profiling
Several misconceptions prevent organizations from effectively implementing threat profiling:
- “It’s just a buzzword that most teams can’t implement.” – In reality, organizations of all sizes can implement threat profiling at appropriate scales. It could be as simple as prioritizing defenses that bolster your protection against ransomware gangs, allowing you to stay in business.
- “Perfect is the enemy of good” – Many teams get paralyzed trying to create perfect threat profiles. When starting, aim to develop basic threat profiles that deliver immediate value. This may include generic security recommendations (e.g., implement MFA), but they will be backed by threat-driven research that your key stakeholders can’t ignore.
- “The Quality and quantity of data are insufficient.” – With resources like MITRE ATT&CK, Tidal Cyber, and various threat intelligence feeds, more data is available than ever. You can use this publicly available data to craft accurate threat profiles.
- “Profiles must be comprehensive from day one” – Your initial cyber threat profile should be a starting point for further research and continuous refinement. Think of your threat profiles as living documents that you continually update as you gather more data about the threat.
Once you overcome these misconceptions about threat profiling, you can realize the advantages of this analysis technique!
Benefits of Threat Profiling
- Relevance: Organizations can avoid expending resources on irrelevant risks by identifying and focusing on pertinent threats. Threat profiles are specific to threats that may target your organization, not a generic report on the threat landscape.
- Structure and Repeatability: A systematic approach reduces analytical bias, ensuring consistent threat profiles supporting decision-makers over time.
- Evidence-Based Decision Making: Quantifiable data supports clear prioritization. Organizations can back their security investments with research on the threats they encounter.
- Proactive Defense: Anticipating and preparing for potential threats before they materialize enhances the overall security posture. Threat profiles help support your incident response and threat hunting efforts by understanding how an attacker behaves.
Great. You are familiar with what threat profiling is (and is not) and some of its key benefits. The next step is to learn what is included in a cyber threat profile so you can start creating one. Let’s explore the key components all threat profiles should have!
Key Components of a Threat Profile
Threat profiles are like cooking recipes. Although they can vary significantly in their content, they all have the same basic components that a chef can follow to produce a tasty dish.
For cooking recipes, this would include an ingredients list, guidance on preparing the dish (e.g., cooking your meat or using the proper utensils), step-by-step cooking instructions, and a clear picture of how the dish should look when completed.
On the other hand, threat profiles include a threat identification section, tactical and operational intelligence (e.g., TTPs and IOCs), strategic intelligence to provide additional context, and supporting elements that enable action to be taken on the described threat.

Let’s explore each of these key components in turn.
Threat Identification
The first section of your threat profile should contain basic information about the threat you are profiling. This typically involves details about a threat actor, such as APT29, 8220 Gang, or REvil Ransomware, to make the threat profile specific and actionable. However, it could also describe more generic threats, such as malicious insiders.
Along with an identifier and some background information, you want to include the central archetype the threat falls under (e.g., nation-state, cybercriminal, hacktivist) and attributes that can be used to classify it, such as motivation, intention, and capability.
To learn more about threat actors and how to classify them, read Unmasking the Hackers: A Complete Guide to Threat Actors.
Here is what a typical threat identification summary might look like.
| Identifier | 8220 Gang |
| Aliases | 8220 Mining Group |
| Description | A crimeware group known to target cloud infrastructure services, including AWS, Microsoft Azure, Google Cloud, Aliyun, and Qcloud. They deploy illicit cryptocurrency miners at their victims’ expense. |
| Archetype | Cybercriminal |
| Motivation | Financial gain – Medium motivation |
| Intent | Affect the integrity of systems to perform crypto-mining |
| Capability | Low capability |
You should also include the Diamond Model in this section when appropriate. This is a fundamental model in CTI that visually represents the relationships between an adversary, their capability, infrastructure, and the victim.

Using the Diamond Model, you should also aim to link the threat to victims (ideally similar to your organization), the infrastructure seen in previous attacks, and the capabilities the threat is known to deploy.
At this point, you want to keep your diamond model generic and refrain from exploring specific TTPs or IOCs. The threat identification section provides an overview that anyone reading the cyber threat profile can understand, regardless of technical proficiency. Here is an example diamond model you could include in this section

Operational and Tactical Intelligence
Following an overview of the threat, you can then start to include operational and tactical intelligence that can be utilized by your cyber security teams (e.g., incident response, security operations, threat hunting, etc.).
Within the operational intelligence subsection, include Indicators of Compromise (IOCs) associated with the threat. These can consist of IP addresses or domains that the group uses to host its infrastructure, as well as file hashes and filenames of malware that the threat is known to deploy. They can also include the group’s personas, such as social media accounts, email addresses, and Bitcoin wallets.
IOCs are great to include. However, they are often easy for the adversary to change to avoid detection. As such, you want to include intelligence further up the Pyramid of Pain, which is more challenging for an adversary to change and will give you a better chance of detecting them.
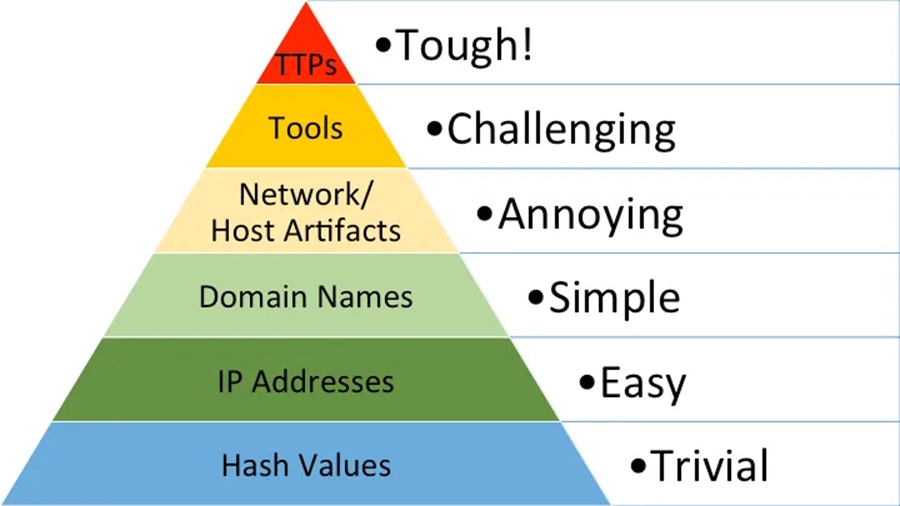
This is where tactical intelligence comes in. Tactical intelligence encompasses the tactics, techniques, and procedures (TTPs) that adversaries employ to execute a cyberattack. These are often included in threat reports using the MITRE ATT&CK matrix as a common language to describe the actions an adversary performed to achieve their objectives.
Including TTPs in your cyber threat profile is essential. They allow defenders to tailor their security controls to detect or prevent the threat you describe.
To conclude this section, you can create a more detailed diamond model that includes the operational and tactical intelligence you discussed (the example below has been redacted for brevity).

Including other visual representations of the operational and tactical intelligence highlighted in this section is also advisable. For example, you could use the Cyber Kill Chain to show a high-level overview of this threat’s typical attack steps or group the TTPs listed under their respective MITRE ATT&CK tactics for a more detailed overview.

An excellent tool to create visualizations using the MTIRE ATT&CK matrix is the ATT&CK Navigator.
Once complete, you can proceed to using strategic threat intelligence to provide the reader of the threat profile with additional context about the threat.
Broader Context: Strategic Intelligence
Threats don’t exist in a vacuum. They are living and breathing entities, just like defenders, who will be affected by geopolitical, economic, and other societal changes. Including this context in your threat profile is vital so you (and the reader) can forecast potential scenarios where this threat may evolve or change.
For instance, what geopolitical events may force this adversary to change its operations? What industry changes may force this adversary to evolve? How will technological changes impact the TTPs that this threat deploys?
To answer these questions, you can utilize an environmental scanning technique such as PESTLE analysis.

PESTLE analysis allows you to assess the external factors that can impact an adversary and their operations by separating macro-environmental factors and analyzing how they may affect them.
Here is an example of a PESTLE analysis performed against 8220 Gang. See if you can think of more environmental factors that could impact this threat.
| Political | Economic | Social | Technological | Legal | Environmental |
|---|---|---|---|---|---|
| Cyber resilience initiatives by the government will push more organizations to improve cloud security. Lowering the target pool. | Lower-cost cloud providers will see more businesses move to the cloud. Increasing the target pool. | Work from home will see more people using the cloud rather than on-premise servers. Increasing the target pool. | Patching vulnerable Linux servers will prevent the initial access methods they use. | Stronger sanctions against crypto-mining gangs will reduce motivation. | … |
| … | … | … | … | … | … |
You can also include a timeline of the adversary’s activity in this section. Again, this provides context for the threat’s rise, the trends it is following, and how its activities have evolved. Make this a visual summary of key events rather than an exhaustive list.
Supporting Elements
The final section of all threat profiles should include links to resources that the organization can use to combat the threat.
You should have already included TTPs that the threat is known to deploy. This section takes it one step further by linking to organizational resources, such as data sources that can be used to investigate the threat, intelligence requirements that match the threat, or detection opportunities (e.g., Sigma rules, YARA rules, or vendor-specific queries).
It is essential to include these links to make the threat profile actionable for those using it and to provide stakeholders with visibility into the actions being taken regarding this threat.
Now that you know the key components every threat profile should include, let’s explore how you can start creating your own threat profiles!
How to Create a Threat Profile
Creating a threat profile is similar to most CTI projects and follows the core steps of the CTI lifecycle. You start with planning, move to data collection, analyze the data you’ve collected, and then produce an intelligence product that a key decision-maker can take action on.
When it comes to creating a threat profile, these five steps are:
- Scope, Objectives, and Data Collection Planning – planning
- Identify Threats – collection and processing
- Prioritize Threats – analysis
- Build a Threat Profile – analysis
- Action Your Threat Profile – dissemination and feedback
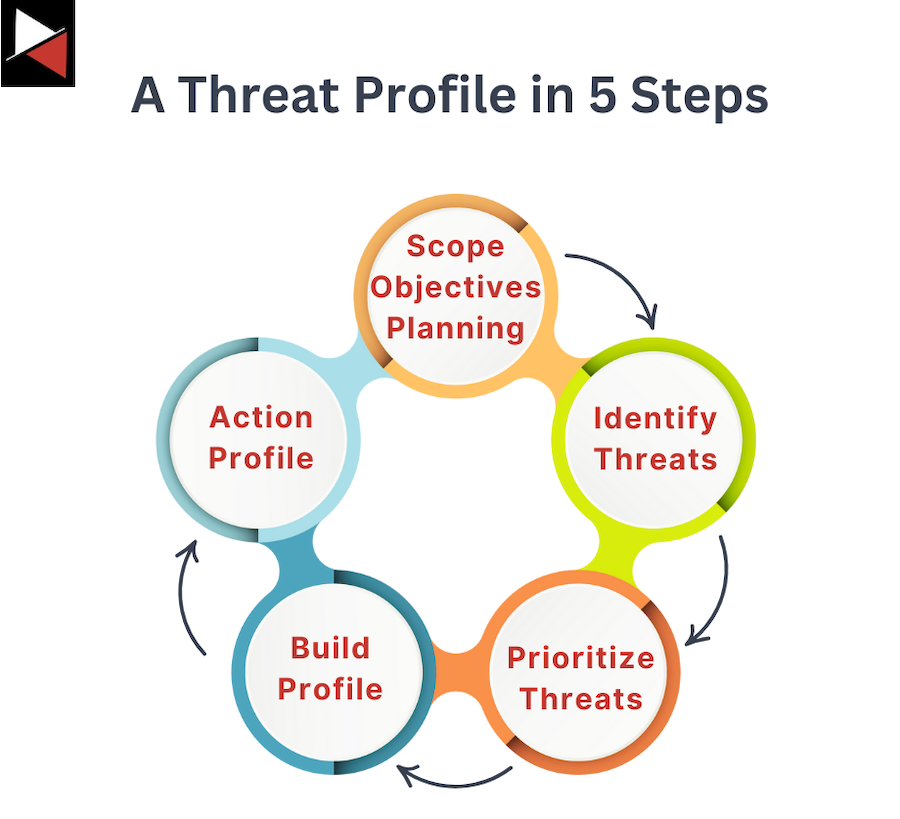
Here is a breakdown of each step. Use these as a guide when creating your threat profiles.
Step 1: Scope, Objectives, and Data Collection Planning
As with all CTI projects, planning is an essential first step. You must decide on several things to plan your threat profile work.
What is the objective of creating the threat profile
Questions to ask:
- What are you hoping to achieve by creating this threat profile?
- Is it to deliver actionable operational and tactical intelligence that the security operations team can use? Is it to track a threat actor?
- Is it to support a high-level overview of the threat landscape for executive leadership?
Deciding on the objective(s) will help you plan what data you need to collect.
Data sources available for collection
Questions to ask:
- What internal and external data sources do you have access to that you can collect data from to build a threat profile?
Ensure that you include both internal data sources (e.g., past incidents, logs, reports, organizational knowledge) and external data sources (e.g., threat feeds, OSINT, dark web monitoring).
These data sources, and what they can be used to answer, may already be included in your CTI team’s intelligence collection plan. If you don’t have one, create one!
Collection strategy
Questions to ask:
- How will you collect the data from your data sources?
- Are you going to browse through it on the web and capture the web pages in an OSINT investigation tool like Zotero, Hunchly, or a web clipper for a notetaking app?
- Will you use an API or web scraping to pull the data?
- Where will you store all this data?
- How will you collaborate on data collection?
Scope of data collection
Questions to ask:
- How much data will you collect?
- Will your scope be time-bound or bound by your data sources?
- Will you pivot to investigate adjacent threats?
Makeup of threat profile
Questions to ask:
- What do you want to include in your threat profile?
This will be determined by the objective(s) of your threat profile. Still, based on the stakeholder you are supporting, you will typically focus more on operational, tactical, or strategic intelligence. Remember, don’t do intelligence work for the sake of doing the work! Ensure you are fulfilling an intelligence requirement that aligns with a business objective.
Sharing your threat profile
Questions to ask:
- What is the dissemination method(s) you will use to share your threat profile with stakeholders?
- Is it a report, presentation, debrief, or a message on Slack or Teams?
- What cadence will you share your threat profile (an ad-hoc report, a monthly update, or an annual summary)?
You may want to share your threat profile in a structured format using a technology like STIX/TAXII. This will allow you to share your cyber threat profile more efficiently across threat intelligence platforms (TIPs) and with the wider community.
Threat profile storage
Questions to ask:
- Will you store the threat profile on a document-sharing platform, such as SharePoint or Google Drive?
- Will you store it in a threat intelligence platform (TIP), such as MISP or OpenCTI?
How you store your threat profile will be dictated by the objective(s) of creating it and how accessible you want to make it.
You can answer these questions using structured brainstorming, either in a group or individually. I recommend engaging in divergent thinking first, which will allow you to generate a range of answers, and then using convergent thinking to narrow down to a specific answer. Then, you can formalize these answers in a work plan or using a Work Breakdown Structure (WBS) that outlines the steps to complete the project.
You can use a Collection Management Framework (CMF) to organize your data sources and collections. This will list your available sources and what questions they can help answer. It can also be reused when creating additional threat profiles.
With your plan in hand, you can move on to identifying threats relevant to your organization.
Step 2: Identify Threats
Once you have a plan, you can begin identifying threats that are relevant to your organization. To do this effectively, you need a general understanding of your business.
You must be aware of the following:
- The business’s mission, objectives, and revenue-generating assets.
- What critical assets exist (crown jewels), the technology being used, and any significant technological changes that have recently happened or are in progress (e.g., remote work).
- The security controls deployed, your visibility into your environment, and the cyber security processes in action.
Identifying these key business components falls under IPCE analysis as part of determining your operational environment. However, if you are short on time, you don’t need to perform a complete IPCE analysis to gain a basic understanding of these components and recognize what threats are relevant to you.
So, how do you identify relevant threats? This is where your data sources from Step 1 come in.
A threat is anything that has the intent, capability, and opportunity to target your organization. Based on the proximity of a threat to your organization, you will have direct threats, industry threats, and opportunistic threats:
- Direct Threats: These are adversaries known to have impacted your organization based on internal telemetry and historical incident data. You have directly observed these threats targeting you, and they should be the first ones to be included in your threat profiles.
- Industry Threats: These threats originate from attacks targeting organizations within your industry, sector, or a similar company. This knowledge is derived from private sharing circles (e.g., ISACs, public-private collaborations), commercial vendor reporting, and open-source threat reports. You will surface the most significant number of threats from this bucket.
- Opportunistic Threats: The rise of cybercrime as a service (e.g., RaaS, InfoStealers) has led to an influx of opportunistic threat actors who target any vulnerable system. They are victim agnostic and will scan for any vulnerability they can find, pillage leaked credentials from the dark web, or buy access from initial access brokers.
Begin your list of relevant threats with direct threats and work your way down to opportunistic threats. Aim for a list of 10-20 groups or campaigns to keep your list of threats “manageable.” That said, you may need to adjust this number to match the resources available to you within your organization.
Using these three buckets and the data sources you identified in Step 1, you can explore threats that are relevant to you with a Google search. However, to save time, it’s often more efficient to use a CTI vendor that aggregates various threat intelligence sources into a platform you can search through to find relevant threats.
Here are some common platforms you can use to perform this research:
- Tidal Cyber Groups
- MITRE ATT&CK Groups
- AlienVault OTX
- EDTA/ThaiCERT: Threat Encyclopedia
- MISP Threat Actor Galaxy
- SecureWorks Cyber Threat Group Profiles
- Palo Alto Unit42 Playbooks
- CrowdStrike Adversary Industries
- APT Groups & Operations (public Google sheet)
Again, start with the threats closest to you and work up to trending opportunistic threats, such as prevalent Ransomware-as-a-Service (RaaS) threats or widely deployed Information Stealers. Once complete, you should have a list of relevant threats prioritized based on their proximity to your organization. You can split these groups into individual threat profiles for analysis.
Splitting groups into threat profiles allows you to manipulate the threat data to find answers to investigatory questions. This is often accomplished using data analysis techniques such as correlations, aggregations, and frequency analysis.
Step 3: Prioritize Threats
Often, splitting threats into the three proximity-based groups mentioned is enough to get you started prioritizing which threats to focus on. However, sometimes you may struggle to differentiate between two threats within a single group. For example, should I choose this InfoStealer or that one, or is APT29 a more relevant threat than APT31, given that I’ve seen both target my industry?
Answering these questions requires an additional prioritization step.

There are several ways you can rank or prioritize the threats you surfaced:
- Critical Thinking: Ask why that adversary would target you? Is it based on their past exploits? Is it based on the technological stacks they commonly target? Is it based on your relationship with a third party? The key is to think more broadly about why you might become a target of this threat.
- Metrics: You can use roughly consistent metrics to see which threat may target you when deciding between two similar ones. For instance, which ransomware gang is most likely to target you based on statistics on Ransomware.live?
- Capability: Narrow down threats based on their capability to attack you. Have they demonstrated a capability that you can’t currently defend against? You should probably prioritize them.
- Leadership Priority: If all else fails, you can ask leadership what they want to prioritize. Depending on your leadership team, this answer may be insightful, based on years of experience, or it may be political and focus on what they want to report to stakeholders, or it may be lackluster.
At the end of this step, you should aim to narrow your list of 10-20 threats to 3-5 high-priority threats for which you need to create a threat profile immediately.
Step 4: Build a Threat Profile
Now, it is time to build your threat profiles. You should have a workable list of 3-5 high-priority threats for which to create threat profiles. Using this list, complete the key components of a cyber threat profile as outlined.
Start with your threat identification section by providing a high-level overview of the threat and a generic diamond model to represent its relationship to the victim(s), infrastructure, and capability. Then, add your operational and tactical intelligence section, describing how the adversary performs attacks. Map these details to the MTIRE ATT&CK framework and include a kill chain to highlight what the threat does at each stage of an attack.
Next, strategic intelligence should be added to provide a broader context. This should include environmental factors that may impact the threat or your capability to defend against it. Finally, add your supporting elements that tie this threat to actionable next steps you or your team can take to protect against it. This includes intelligence requirements, data sources, and detection opportunities.
Perform these steps for each of your top priority threats. Once complete, you can use these threat profiles to perform data analysis, correlation, and pattern recognition to uncover intelligence insights.
Some of these insights could include:
- What TTPs are the most common across threats?
- Are threats linked in any way?
- Are there common patterns in initial access?
- Can you prevent all the TTPs identified? Are there gaps in logging, intelligence, or detection?
- What commonalities exist in the infrastructure used to perform attacks?
- Can you identify trends across threat profiles?
- Are there common environmental factors that impact multiple threats you should monitor?
- Can you test the capabilities identified for each threat against your current security controls? You could use the Atomic Red Team project or adversary emulation platforms like VECTR.
Here is an article on how to correlate TTPs between threat actors to find the most common ones relevant to your organization. Threat profiling makes this intelligence insight possible.
Next, you can proceed to the dissemination stage of threat profiling, where you share your threat profile with security teams so they can take action.
Step 5: Action Your Threat Profile
The final step of threat profiling is sharing what you created. Based on your planning in Step 1, you should know the stakeholder(s) with whom you will share your threat profile, the mechanisms for sharing, and where you will store it once shared.
To recap, depending on the stakeholder(s), you may need to adapt the format and structure of your threat profile to suit their needs. For instance, a C-level executive will want a high-level summary to prepend the threat profile. This allows them to grasp the report’s gist without wading through technical details. Add or remove operational, tactical, and strategic intelligence to suit your audience.

You should also consider how you will maintain the threat profiles you create:
- How will you update them?
- How regularly will you update them?
- Will you use version control?
- How will you communicate updates?
- Who can access them?
- Who can edit them?
These are some of the questions you must answer when considering the storage and maintenance of your threat profiles. If you make your threat profiles available to internal employees, you could stick them on a SharePoint site or Google Drive. However, if you plan to share them with the wider community, you might need to use a TIP, version control tools like Git, or another solution.
MITRE’s CTI Blueprints project is a great, free tool for creating threat profiles. It includes a web-based GUI for creating a Threat Actor Profile, which can then be automatically converted into a PDF or Word Document for sharing.
Of course, the sharing mechanism you will use must be considered. This heavily depends on who you want to share the threat profile with. Still, whatever method you choose must be secure, deliver the threat profile in a timely manner, and ensure it is accessible for those with neurological differences.
Here are some standard sharing mechanisms used for threat profiles:
- Ad-hoc reports that are sent via email.
- Monthly, quarterly, or annual updates over email or instant messaging.
- Debrief calls (ad-hoc or scheduled).
- Published on a blog or website.
- Published internally (e.g., Workplace, TIP).
- Share via a TIP using STIX/TAXII.
The format, storage/update process, and the sharing mechanism you choose should support making the threat profile actionable. They should empower the reader to become knowledgeable in threats relevant to the organization, identify gaps and priorities, and recreate adversary behaviors to validate their security controls when necessary.
This “actionability” and the quality of the threat profiles being produced should be measured and fed back to the CTI team so they can continuously improve their process and the threat profiles they create.
Conclusion
Threat profiling transforms how organizations approach cyber security by focusing resources on adversaries most likely to target your specific environment. This targeted approach strengthens your security posture while maximizing return on security investments.
Remember that threat profiles aren’t static documents but living resources that should evolve with the constantly changing threat landscape. Implement regular reviews, incorporate new intelligence, and continuously refine your understanding of relevant threats.
Start small if necessary. Even basic profiles covering your most significant threats provide immediate value. As your practice matures, you’ll develop deeper insights into adversary behaviors, identify patterns across threat actors, and anticipate emerging threats.
Effective cyber security isn’t about having the most tools or the biggest budget. It’s about identifying which threats matter most to your organization and tailoring your defenses accordingly.



Frequently Asked Questions
What is Threat Profiling in Cyber Security?
Threat profiling is a structured methodology for identifying, analyzing, and documenting potential adversaries and their capabilities. It helps organizations understand who might target them, why, and how, using operational, tactical, and strategic cyber threat intelligence. These details enable defenders to be more targeted and effective in their defense.
What is a Threat Profile?
A threat profile is a living document that captures essential information about a specific threat or threat actor, including their motivations, capabilities, typical tactics, techniques, and procedures (TTPs), indicators of compromise (IOCs), and historical activities. It serves as a reference for security teams to better understand and defend against potential threats.
What is Threat Analysis?
Threat analysis is the process of examining potential threats to identify patterns, capabilities, and likely targets. It involves collecting and analyzing data from various sources to understand the tactics, techniques, and procedures (TTPs) of threat actors, ultimately informing security strategy and operations. Threat analysis often yields a comprehensive threat profile.
Threat Profiling vs Threat Modeling – What is the Difference?
Threat profiling focuses on the adversary, answering “who” might attack you and “why” by analyzing a threat actor’s motivations, intent, and capabilities. In contrast, threat modeling focuses on your own systems, answering “how” and “where” you are vulnerable by systematically identifying and evaluating potential security threats and weaknesses from an attacker’s perspective. Essentially, profiling studies the attacker, while modeling studies your potential attack surface.
Where Can I Find Threat Actor Profiles?
You can find publicly available threat actor profiles from several authoritative sources. The MITRE ATT&CK® Groups page provides a comprehensive knowledge base of known cyber adversary groups and their documented techniques. Cyber security vendors like CrowdStrike also maintain a public adversaries page detailing the actors they track, while platforms such as the Tidal Cyber Community Edition offer tools to explore and compare intelligence on a wide range of threat actors
Threat Actor Profiling vs Cyber Threat Profiling – What is the Difference?
There is often no significant difference, as the terms are frequently used interchangeably. However, when a distinction is made, Threat Actor Profiling focuses narrowly on the human adversary, analyzing who they are, their motivations, and their capabilities. Cyber Threat Profiling can be a broader term that includes the actor but also encompasses the full technical scope of a threat, such as the specific malware, vulnerabilities, and infrastructure used in their operations.